24 April 2023
security posture
Security posture
The security status of an organisation’s networks, information, and systems based on cyber security resources (e.g., people, hardware, software, policies) and capabilities in place to manage the defence of the organisation and to react as the situation changes.

Industry News | 24 October 2023
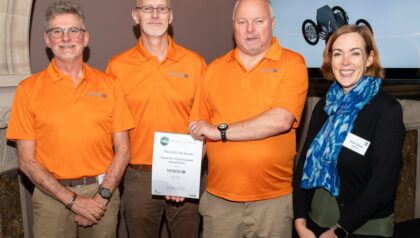
eCall project wins TRIG award for its innovative proven idea
VESOS Solutions Limited has been recognised for the value of their solution giving emergency services and road operators […]
Read more
Industry Events | 24 October 2023
Launch Of The ITS Exports Study
Join us for the launch of a new study exploring the export priorities of the UK ITS sector. […]
Read more
TTF News | 24 October 2023
ITS UK announces export study launch
9th November 2023, London
ITS UK has announced the launch of a new report, developed in partnership with the Department for Transport, […]
Read more
News | 19 October 2023
£70m signals funding timescales announced
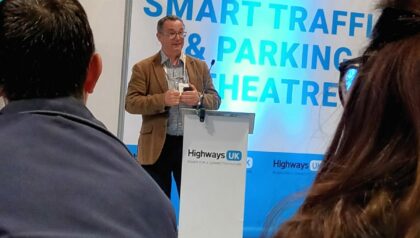
The manager of the Transport Technology Forum (TTF), Darren Capes has given more details about the process of […]
Read more